Category: Articles

  • Submission to the Inquiry into cyber security for small to medium sized businesses and organisations

    Submission to the Inquiry into cyber security for small to medium sized businesses and organisations

    Australian small and medium businesses (SMBs) are widely seen as more vulnerable to cyber security incidents and crime. To better understand the issue and find directions for new solutions, the Australian House of Representatives voted to create a Select Committee on Cyber Security for Small to Medium Sized Businesses and Organisations.

    The Chair of this committee, Sally Sitou MP, described it as the first federal inquiry to specifically examine this issue for small businesses, noting that “small businesses are on the frontline of cyber risk but too often they’re expected to defend themselves without the time, tools or resources they need.”

    This committee received bipartisan support, with the Shadow Minister for the Digital Economy, Aaron Violi MP, calling it an “important committee” and putting forward a supportive proposal for a member of the Opposition to be deputy Chair, which was accepted by the Government.

    We provided a submission to the Committee to share what we’ve learnt about this problem in our work at Lumenas, and put forward a range of proposed actions for government, the business community and industry associations to address this issue systematically. Lumenas provides one part of broader solution through our tools for accidental IT leaders, but we think there’s more work to be done across the economy so small businesses are better supported.

    To read our full submission click here.

  • Working with an IT Provider

    Working with an IT Provider

    For many businesses, especially those under 200 staff, your IT provider is one of your most critical vendors. They hold the keys to all of your data, and when IT stops, the business stops. Despite that, most businesses I speak to take a very light touch to managing this relationship. Often the job sits with the ‘accidental IT leader’. This is someone whose real role sits in operations or finance, but because they’re so good at keeping things running, they’ve been handed a few extras. IT is one of them.

    Usually the original agreement has expired, or it never had much detail to begin with, so it no longer reflects what the provider actually does for the business today. The monthly or quarterly check-ins stay focused on the operational. Tickets, outages, the printer on level two.

    So how do we know if we’re doing enough for the organisation when it comes to IT?

    Firstly, let’s not focus on perfect – I’ll write some more in the future about dialling in technology for your organisation. Most organisations would be well served to start with the basics; are you and your provider on the same page about what is actually happening? And are they following best practices?

    One of the reasons for the uncertainty is that IT, like law or accounting, carries a serious information asymmetry. Your provider has likely spent years learning their trade, and there’s no clear guide for you, the customer, on what good looks like. But unlike law or accounting, IT doesn’t come with strict professional standards or consumer protections to fall back on.

    So to break down some of that asymmetry, I want to share what I see in organisations where this relationship is working well, and some of the signs that things might be off track.

    What good looks like

    • You meet regularly with your account manager, or perhaps even the business owner.
    • You get the sense they understand how your business works, and how their services support it.
    • You receive written reports that show evidence of the work being done, in a form you can actually read and interpret.
    • Your agreement is detailed, current, and you’ve read it.
    • And at some point, you’ve had an independent set of eyes assess your security, or confirm the services you’re paying for are the right fit.

    Signs things might be off track

    • You can’t find a copy of the agreement at all. Or you can find it, and it’s under two pages, with no service level agreements and little detail about what the provider actually delivers.
    • No one meets regularly with the person who manages your account.
    • Your meetings are full of technical jargon, and you leave confused or frustrated.
    • And the only checks you’ve seen on security or performance have come from the provider themselves.

    None of these are reasons to panic, but they are signs to dig a little deeper.

    Take action

    We’ve built a tool that helps organisations understand what’s really happening in their IT, and whether they and their provider are on the same page. It’s called the Lumenas End-to-End IT Check. It produces a shared responsibility view showing what your provider covers, what sits with you, and where the gaps are. All in a short report you could take to your CEO or board.

    It takes one hour of your time, and not knowing the answers going in is the whole point. We’re looking for accidental IT leaders who want more clarity. Two weeks from now, you could have a clear picture of where things stand and how to move forward, in board-ready language, without needing a technology degree to read it.

    Find out more here, or email hello@lumenas.com if you’d like to speak with us about how to get more from technology in your organisation.


    This piece was originally published here on Linkedin as part of the Leading Digital series from Longitude Advisory.

  • Why are you doing the office housework?

    Why are you doing the office housework?

    I once eagerly joined a work-extra-curricular group that used data analysis to support greater diversity and inclusion. I thought this would be a great opportunity to make something more constructive than cupcakes for International Womens’ Day and make the workplace more inclusive for lots of people. I did not anticipate this would lead to me incite a small riot in the team chat only a week later.

    There were concerns about coaching assignments, I learned, in my first meeting with this work-extra-curricular group. Apparently there was a growing perception that junior women were intentionally assigned to mid-career women coaches, simply because they were women – not because the match otherwise made sense.

    I spoke up: surely this was the lesser of two evils? Of course, there was the chance this was not a good match for junior women, but mid-career women certainly had much higher coaching loads. The talent pipeline for women strongly resembled a squished triangle – how could that ratio of mid-career to junior women possibly be fair in this coaching context? At this point in the conversation, it was still perception and conjecture, so I volunteered to analyse the data.

    The data showed that I was right and had also missed the bigger problem. Mid-career women indeed had relatively more women coachees; but also relatively more male coachees. Overall, they were doing roughly double the coaching workload of their male counterparts. I dutifully copied this analysis into the internal comms channel which I’d been told was the relevant forum for feedback and discussion.

    Coaching itself is not bad, I argued back in the early eruption of indignation from my colleagues as messages began to pour in. It can be beneficial for all involved, and for many women who feel this greatly supported their career paths it makes sense to give back. My colleagues were clearly divided into two groups: those arguing I didn’t know what I was talking about and those furiously copying in links to articles about office housework.

    Office housework became better understood through a 2017 paper in the American Economic Review. The paper found that women, more often than men, receive and accept requests for tasks with ‘low promotability’.

    This highly unequal coaching workload seemed like a pretty clear example of this problem. Coaching, in this instance, was necessary but no one got rewarded or recognised for this work, much like unloading the dishwasher. But this was partly because of how coaching was often done in this organisation.

    There are some instances of coaching that are highly valuable to the coach (even if it’s unpaid). Coaches can learn new things from their younger counterparts, including those who may have different strengths or experiences. There is also significant value in building a strong network of great people you can promote and hire in the future. The extra office housework is problematic, but while evening the load, women can also be more strategic about what tasks we accept.

    There are select tasks at work that superficially meet the definition of ‘office housework’ (no one wants to do it, but they absolutely need to get done and appear to have low promotability), but are secretly strategic opportunities. IT is a good example.

    In very large organisations, this is already looked after by IT departments, CTOs and CISOs. But sometimes there can be opportunities to join employee representative groups or ad hoc projects, like figuring out how AI is useful for your area. These aren’t quite a goldmine of strategic opportunity, but they’re a pretty solid silver.

    IIn all other organisations, IT is a goldmine of strategic opportunity. If you leverage this well, you can:

    • Use it as an opportunity to write a strategy that actually gets implemented – this doesn’t have to be long or complicated, it just needs some ROI (including positive feedback) you can use in your next job interview.
    • Use it as an opener for a listening tour – by leveraging your strategy as an opening to have coffee and learn from more senior people in your field who have also been accidental IT leaders (as long as your current boss is fine with any organisational information shared as part of this tour).
    • Use it as training for managing people with skillsets that are different to yours (like your external IT vendor) – this is one of the hardest things to learn at work, and it’s also rare (but highly valuable) to get experience in this before becoming super senior.

    I’m learning that IT is frequently managed by accidental IT leaders, many of whom see it as office housework. We also know that tech is grossly underutilised in lots of small and medium organisations. Instead of telling these time-strapped small teams to get ‘smarter’ about tech, let’s empower accidental IT leaders with the right training and tools to be more strategic about managing tech for their organisation and themselves.

    At Lumenas, we’re working on making better tools for accidental IT leaders. If you’re an accidental IT leader, or you’d just like to learn more about this problem, let us know at hello@lumenas.com


    This post was originally published on Linkedin here.

  • Ice Cream Shop or Military Base?

    Ice Cream Shop or Military Base?

    Cyber security can often feel like a game of absolutes — either we’re secure or we aren’t. But it’s more complicated than that. The answer is almost always that we’re somewhere in between.

    Cyber risk, like all other risk, exists on a spectrum. We have to decide how much risk we can tolerate, then apply treatments and other mitigations to close the gap. Determining that tolerance is one of the most important technology decisions boards and executives make — it informs the whole cyber security program.

    But how do we know what our risk appetite is?

    One discussion exercise I run with organisations helps find the answer. Everyone in the room gives a number from 1 to 5 describing the organisation’s ideal cyber risk posture. One is an ice cream shop. Five is a military base.

    The purpose isn’t to land on some point in between that describes us perfectly. The purpose is to have an open conversation about the kinds of risks we face, the ways we use technology, and how much tolerance the business has for disruption.

    Take the ice cream shop. We’re probably taking digital payments and using some systems for ordering ingredients and managing staff, but we aren’t storing sensitive customer data. If we go offline, we can keep operating on cash, or take payments from a backup mobile terminal. Cyber hygiene still matters, but security may not be a major area of investment. Even at the low end the basics are non-negotiable — the scale starts from one because no one is at zero.

    Now think about the military base. Security is top of mind. We’re storing extremely sensitive information, and we need assurance that it hasn’t been accessed without authorisation or altered. The success of our information systems can be a matter of life and death — we rely on them for far more than information storage, from accessing controlled stores to communicating time-sensitive orders and managing access by identity and clearance. Here there’s serious investment in a layered security program that is continuously monitored, reviewed, and improved.

    Most of the organisations I work with land somewhere in the middle. The exercise gives us a group conversation that can challenge assumptions and build a consensus on what our ideal posture looks like. Usually we start with a few different positions in the room — some say three, some say five — and over the course of the discussion we work out why those positions were chosen. I’m yet to work with a group that couldn’t reach a consensus to carry forward into the decisions that follow.

    From there, I most organisations benefit from formalising the output of that discussion in a risk appetite statement. That can be used alongside governance activities like reviewing cyber risk assessments, developing treatment plans, or shaping an organisational cyber security program. As leaders, we can direct investment more confidently and understand the trade-offs we’re making with risk because we’ve had a clear conversation about what it actually means for our organisation.


     This article was originally published here on Linkedin as part of the Leading Digital series from Longitude Advisory.

  • Moving beyond digital transformation

    Over the course of decades, we’ve come to expect digital transformation to be a big event. These transformations are typically incredibly slow and expensive and the failure rate is astronomical. The impact on employees is serious, with each new wave of major changes adding to change fatigue, and sometimes mistrust if the transformation doesn’t deliver the proposed benefits.

    It’s time to change our approach. We can move from large-scale transformation to smaller adaptations as the world, and technology, changes around us  – instead of transformation, an evolution over time.

    Evolving to fit a changing world

    The process of digital transformation is unwieldy and exhausting – for those executing it and for those being constantly change managed. Big budgets and project management overheads see these large scale transformations embroiled in organisational politics and red tape. They also make them turn about as gracefully as a cruise ship in response to change. Perhaps the biggest challenge is that digital transformation is usually seen to have an ending. The teams roll off the program, the budget line ends, we are transformed.

    This approach is inherently flawed. The business needs continue to change, customer expectations move, and the team changes the ways they work and use technology – nevermind the changes in the technology itself!  In the old model, we let the needs continue to drift from our technological reality until it’s time for another transformation.

    There’s a different way to think about technology change. Rather than these monumental transformations, we can build organisations that are in a constant state of technological evolution.

    In organisations that embrace technological evolution, staff are adaptable, lifelong learners who embrace the opportunity to improve systems and processes as opportunities arise. Technology leaders and teams are engaged in problem solving as part of normal business, in partnership with teams across the organisation. Leaders can adapt quickly to new opportunities, like AI, because they are accustomed to evaluating new opportunities quickly and rigorously. They have guardrails for risk and a clear picture of ROI.

    In a digital evolution model, we do not wait until a system is completely broken, a process is deeply inefficient, or a risk has become urgent. We notice the early signs of drift and empower teams to adjust.

    Living governance is the key to making digital evolution possible. An organisation’s ability to continually understand whether its technology needs are changing and if its environment and tools are keeping pace, alongside clear guardrails so that teams can make change without huge overheads.

    Living governance

    The problem I run into most often is that leaders cannot govern what they cannot see and understand.

    During a transformation project, there is usually a lot of visibility. Either the internal team or a consultancy comes in and creates all the elaborate documents: current-state assessments, future-state designs, system inventories, roadmaps, risk registers, process maps, business cases.

    That point-in-time work usually ends up out of date and on a shelf very quickly.

    If we want to move from transformation to evolution, we need a living view of the technology environment. A way to see how technology connects to the things leaders actually govern: risks, vendors, costs, obligations, performance and strategic priorities.

    I’m not talking about documentation for its own sake (see the previous article on security theatre), or a technical catalogue that only IT can understand. Digital evolution relies on access to actionable information in real time, and a shared set of rules that democratise change at the lowest practical level of an organisation. It should help leaders see:

    • What has changed?
    • Is our environment fit for purpose today?
    • What about next year? Is our spend aligned with our priorities?
    • Are we within our risk tolerance?
    • What does good look like?

    If leaders cannot see the small issues, they cannot make small adjustments. Similarly, if teams need to wait for organisational leadership intervention to make adaptations, then small adjustments just aren’t practical. The small issues continue to accumulate.

    Then, eventually, the gap between the business and the technology becomes too big to ignore, and the organisation needs another major transformation. We’re back on the merry-go-round again! There’s a way to break out of that cycle.

    Digital transformation changes an organisation. Digital evolution keeps the organisation operating effectively in a changing world.

    Can you see your environment clearly enough to ask those questions and make adjustments?

  • Stories from the basement: how fictional IT leaders shape our perception of IT leadership

    Stories from the basement: how fictional IT leaders shape our perception of IT leadership

    Early in building Lumenas, we found ourselves often reading job advertisements for IT Managers. Not because we were hiring, but because job ads are a frank assessment of what an organisation thinks a role involves. This helps us better understand the misunderstanding of IT roles, and how persistent these issues may be, which helps us better design our products which help close this gap. 

    Looking at job ads helped us check whether anecdotal experiences were more systematic. Do organisations persistently misunderstand what IT leaders do? We expected this would probably be the case, but we were struck by the consistency.

    The most consistent gap we noticed was the near-total absence of governance. The technical requirements were detailed, but the leadership and management expectations were vague. Based on the job descriptions we looked at, you would expect people in these roles to be tactically proficient, highly responsive but rarely proactive. 

    We know this isn’t an accurate depiction of what IT leadership requires, or looks like, in reality. This gap in the perception and reality of IT leadership is probably shaped by a number of factors. One factor that seemed worth better understanding was the role of pop culture.

    Pop culture significantly shapes our perceptions of careers. Perhaps most famously, the release of the original Top Gun move inspired a nearly 10% increase in US Navy recruitment. The portrayal of particular occupations shapes our expectations about jobs and the people in them.

    To better understand how Western pop culture has shaped our perceptions of IT careers we decided to start a weekly series in which we’d analyse iconic IT characters.

    Six weeks, six characters, five questions

    We spent six weeks analysing fictional IT managers to better understand how pop culture portrays the role and how those portrayals might be shaping the expectations of the people who hire, manage, and work alongside IT leaders.

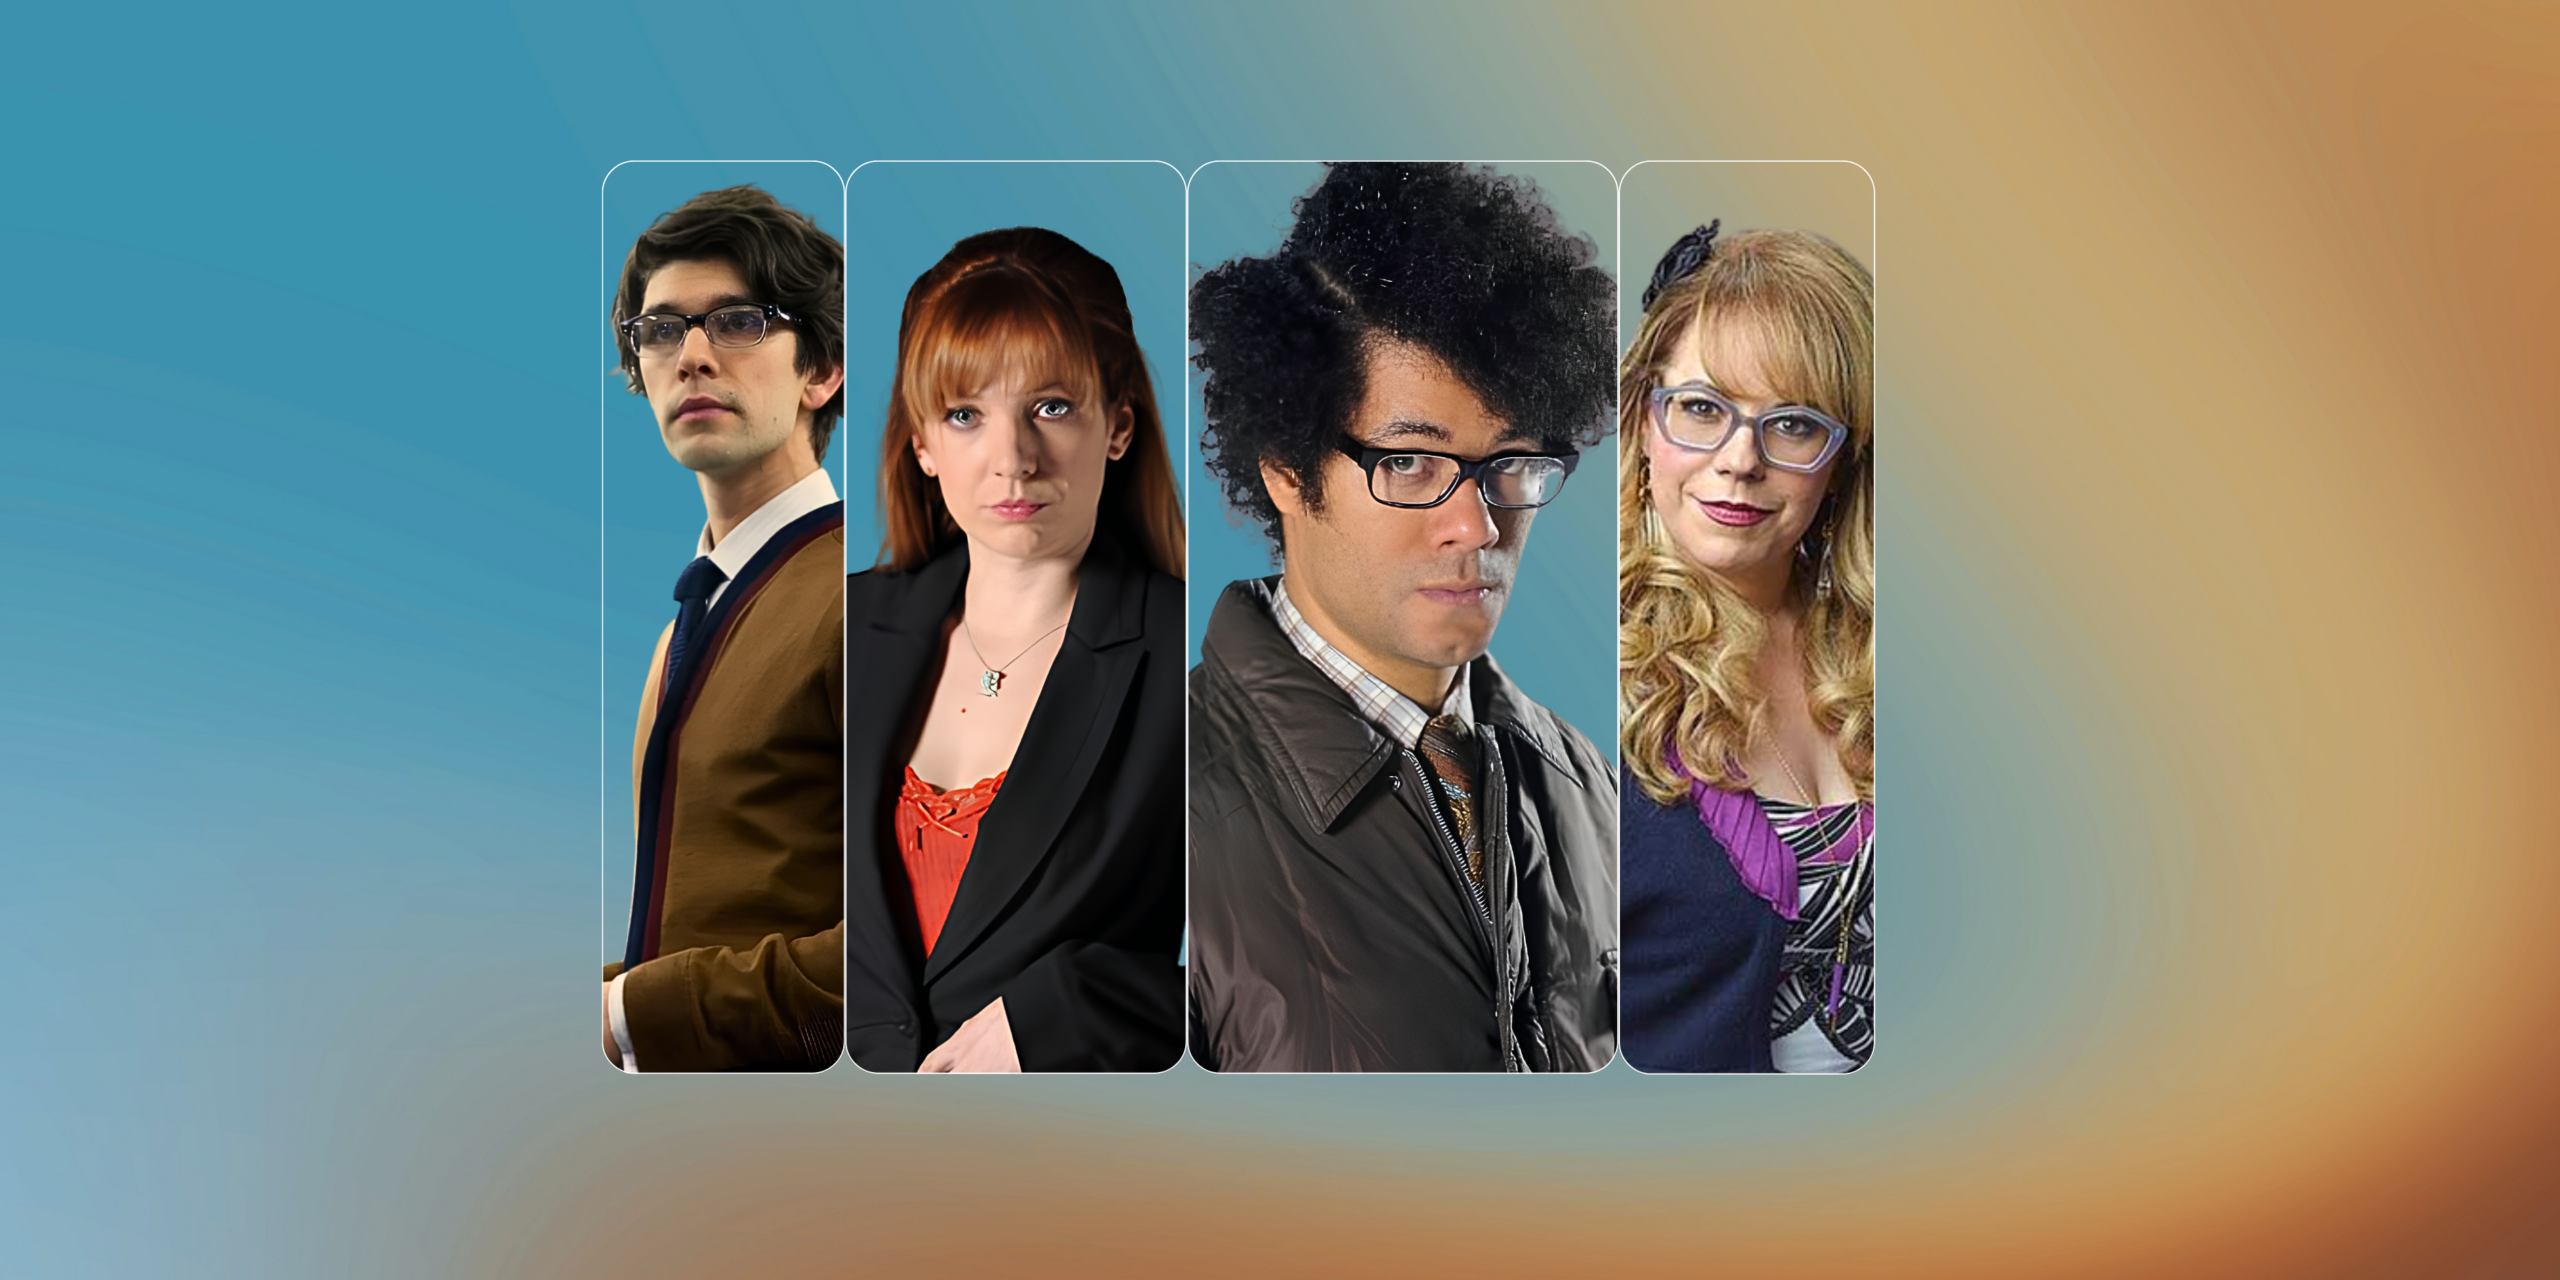
    We chose six characters: Moss and Jen from The IT Crowd, Gilfoyle from Silicon Valley, Abby from NCIS, Penelope Garcia from Criminal Minds, and Q from the James Bond franchise. We asked the same five questions of each character.

    Is this character a punchline or a person? We wanted to know whether the show treated its IT character as a fully realised human being, or as a recurring joke. The distinction matters: a character who exists to be laughed at teaches the audience something different about IT than one who is shown to have depth, growth, and genuine relationships.

    Is this a realistic portrayal of IT leadership? Not technically accurate (we weren’t looking for accurate depictions of network architecture) but realistic in terms of what IT leadership actually involves. Does the character deal with stakeholders? Manage ambiguity? Operate under constraints? Or does technology simply work like magic whenever the plot requires it?

    What cultural value does this place on IT? Is IT work portrayed as cool, respected, and consequential? Or as something slightly embarrassing; tolerated rather than valued? This question gets at the status the show implicitly assigns to the role.

    How mature is this character’s IT leadership? Are they reactive – fixing things when they break – or are they building systems, developing people, and shaping the direction of their organisation? We scored this on a spectrum from firefighting to force-multiplying.

    How likely are they to adopt Lumenas? We included this partly for marketing purposes but also because it forced us to think concretely about each character’s relationship with management tools. If presented with a tool that would require you to actively opt into thinking strategically about the business of IT, would you welcome it? Or shun it?

    Asking the same five questions across six characters gave us a simple basis for comparison, and pushed us to think about each character in more depth than we had as fans. This helped us learn a few things upon observation and even more upon reflection.

    What we learned

    The Peter Pan problem

    Almost every fictional IT character is frozen in time.

    Moss never learns to navigate the world outside his server room. Penelope delivers results at impossible speed across fifteen seasons but never builds a team or a system that could outlast her. Abby is the most competent person in the building, but the show never gives her adequate resources or support. Gilfoyle refuses to manage anyone and is rewarded for it. Q equips Bond and disappears. Jen tries to grow and is consistently humiliated for the attempt.

    In fiction, IT characters don’t grow up. The comedy, the drama, the narrative tension; it all depends on them staying exactly as they are.

    We called this the Peter Pan problem.

    The parent-child paradox

    There’s a second pattern that runs alongside the first, and it’s a weird twist.

    These characters are simultaneously infantilised and expected to parent everyone around them. They’re treated as oddities — socially awkward, professionally misunderstood, never quite taken seriously. But they are also the person everyone calls when something goes wrong. They’re there to fix it. Without complaint or explanation. They rarely ask for more time, resources or even information.

    The message, repeated across decades of television, is that IT leaders will always be there to save us. Not just because they’re capable — but because that’s ‘who’ they are. 

    That’s an impossible bar. No one can always give. And when the expectation is that IT leaders exist to absorb problems without limit, the question that never gets asked is: what do they need to succeed?

    Who came out on top

    When we scored the six characters across the first four questions — leaving aside the Lumenas adoption question — Q scored highest. He’s the most realistic portrayal, the most force-multiplying, and the only character in the series who is consistently treated as a peer rather than a curiosity.

    Remove question 5 on Lumenas adoption and Gilfoyle wins. He’s the most accurate portrayal of what real infrastructure work looks like, and the show respects him for it.

    Moss scored lowest by a significant margin. Almost every question landed him at the bottom of the scale. But we also learnt from our posts on Linkedin that Moss is the People’s Choice with the most likes of any character. Looking beyond likes, to see who had the highest engagement, we found that Penelope and Jen tied as the most intriguing of IT characters. More than half of everyone who saw those posts clicked through to read more.

    The contrast between the highest score and most likes taught us something important about the IT community. Technical excellence earns admiration, but genuine effort and good intent earns different kind of trust. No one thinks Moss is a good example of IT leadership, but we love him anyway. It’s hard to think of another profession where capability is so highly valued but honest effort is wholeheartedly prized.


    We hope you enjoyed this series as much as we did. It changed how we think about the gap between what IT leaders are expected to be and what they’re given to work with in most jobs.
  • The Accidental IT Leader

    The Accidental IT Leader

    Becoming an ‘accidental IT leader’ presents a significant opportunity.

    Many business leaders become technology leaders without ever applying for the job. You might start in operations, finance, administration, risk, or another business function. Over time, technology decisions begin to drift your way. You become the person who talks to the MSP, reviews software renewals, helps choose new systems, answers questions about cyber risk, or translates between technical suppliers and senior leaders.

    Suddenly, you’re in charge of technology. If that feels uncomfortable, you’re not alone! Many accidental IT leaders I speak to feel that way. You’re confident managing people, budgets, processes and risk, but still feel unsure when the conversation turns to systems, cybersecurity, AI, data, or technical suppliers.

    Technology can feel full of unfamiliar language, fast-moving trends and decisions that carry serious consequences. When you’re already busy, it’s natural to want to stop at one simple question: “Does it work?” But if technology has landed in your role, there is also an opportunity here. With the right support and a stronger grasp of the fundamentals, accidental IT leadership can become a valuable part of your leadership toolkit.

    You already have more of the skillset than you think

    It’s no secret that most organisations now rely on technology to function. Digital systems shape customer experience, staff productivity, cyber resilience, reporting, compliance and growth. Even relatively small technology decisions can have a large business impact. That means the ability to lead technology well is becoming a valuable leadership skill, not just a technical specialty. The good news is that accidental IT leaders often already have many of the hardest skills to teach.

    You understand how the business works, where processes break down, and the impact on staff and customers when things aren’t quite right. You are used to balancing cost, risk and practicality. You know how to manage competing priorities and make decisions when the answer is not perfectly clear…Those are technology leadership skills, too! Being able to recognise your existing strengths can show you the big headstart you have.

    The missing piece is often not your capability. It is confidence, structure and enough digital literacy to know what questions to ask. This doesn’t mean becoming a technician or some kind of AI expert. It means knowing how to prioritise investment, work effectively with providers, manage risk, and connect technology choices to business outcomes.

    What good accidental IT leadership looks like

    Good technology leadership relies on the leadership foundations you already have: clear priorities, sound judgement, stakeholder management, risk awareness and disciplined execution. The difference is learning how to apply those strengths to technology decisions.

    Good IT leadership does not mean having all the answers. It means knowing what decisions need to be made, who needs to be involved, what risks need to be visible, and how technology choices connect back to business outcomes.

    • It might look like asking your MSP clearer questions about risk and service quality.
    • It might look like slowing down a software purchase until the business problem is properly understood.
    • It might look like bringing cyber risk into the executive conversation before there is an incident.
    • It might look like creating simple guidance for staff using AI tools.
    • Or it might look like noticing that a system is technically working, but creating daily friction for the people who rely on it.

    This is where accidental IT leaders can be especially effective. You are close enough to the business to see what is really happening, and positioned well enough to help change it.

    Two practical steps to better digital leadership

    If IT has organically become part of your role, start by getting clear on what has actually landed with you.

    Are you approving software? Owning the MSP relationship? Answering cyber insurance questions? Making decisions about AI use? Managing system changes? Reviewing contracts? Explaining technology risks to senior leaders?

    Once you have a clear list of your digital leadership responsibilities, build your understanding of the fundamentals around it. That will stop the huge time sink that can result from trying to ‘learn tech’ – there’s just so much out there! Start with which systems matter most, what your providers are responsible for, what risks need executive attention, what data the business relies on, and where technology is creating friction for staff or customers. The goal is to know enough to manage decision-making with confidence and ask better questions of vendors, providers and technology teams.

    The second step is to build a network. Accidental IT leaders should not have to work it all out alone. Find peers in similar roles, trusted advisers, internal champions and providers who are willing to explain, not obscure. A good network helps you test assumptions, sense-check decisions and build confidence over time. It also makes the role feel less isolating.

    Technology decisions are easier to lead when you have people around you who can help you separate what is urgent from what is important, and what is technical detail from what is a business decision.

    A role worth growing into

    Accidental IT leadership can feel like yet another responsibility added to an already full role. If that is your experience, it is reasonable to feel stretched by it. But it can also be one of the most valuable leadership opportunities available.

    The organisations that get the most from technology are not always the ones with the biggest budgets or the most complex tools. They are the ones with leaders who can connect digital decisions to the real needs of the business. For those who have inherited IT, there is an opportunity to become the person who does not just keep technology working, but helps it work better for the organisation.

    That skillset is only becoming more valuable as emerging technologies continue to reshape work and business. A proven track record of leading technology decisions, managing risk and creating positive impact can be a real career boost.

    You do not need to become a technical expert to lead technology well. Our Leading Digital workshop is built for business leaders who have inherited responsibility for IT, cyber, software or digital systems and want a clearer, more practical way to lead. It’s a curated, jargon free, experience giving you a framework and strong digital leadership foundations, without information overload. Visit our website to find out more about the workshop and other resources for Accidental IT Leaders.


    This piece was originally published as part of the Leading Digital newsletter on Linkedin here.

  • The one thing economists love and IT hates

    The one thing economists love and IT hates

    The IT department has often been my first stop in any new job. This is because I often do pretty niche jobs, which means I need a different tech setup to most of the organisation. This has variously delighted and haunted my IT colleagues.

    In one job, I requested different permissions on my laptop so that I could update my special data science software more easily. This kind of software needs lots of little updates (often in the middle of my work) to keep functioning.

    It’s kind of like staying at a hotel and asking housekeeping for a freshly laundered pillow frequently – but not every night – because it alleviates otherwise-debilitating neck pain. Faced with this request, IT has three options: send someone to give me a freshly laundered pillow frequently (but randomly) on short notice, give me the key to the pillow room or give me the keys to every room in the hotel in perpetuity. They chose the third option.

    Why did IT give me the forever-master key to the metaphorical hotel? I would argue it’s because they probably thought the benefits outweighed the costs. This option gives me lots of flexibility to solve my own problems. I could try every pillow in the hotel (I didn’t), check if other people had different pillows to me (I didn’t, I don’t care) or go get a new pillow from the pillow room when I needed one (which I did). Choosing this option also benefits IT because they don’t have to answer my frequent, random emails and deliver each pillow. I also thought less emails were excellent because I’m impatient and urgent requests for a single freshly laundered pillow feel a bit ridiculous, even if there’s a sensible reason.

    But this option has a cost: an unacceptably low level of cybersecurity. While I never went into anyone else’s metaphorical hotel room, it is best practice to not give out master keys to hotel guests at random.

    In this instance, IT could choose this option because we hadn’t explained our preferences regarding cybersecurity, growth or much else. But even if you don’t explain your preferences, they will be revealed to you. Revealed preferences, the practice of identifying preferences through observation is generally the best measure of economic value thus loved by economists, and the worst way of managing tech thus hated by IT.

    IT people viscerally hate learning about a client’s preferences via observation, in my experience. But it’s often challenging to get a clear statement of preferences from non-technical business leaders. So they make-do with the information they’re given and trudge along.

    Some IT providers are able to bridge this tech-business communication gap. Consistently closing this communication gap across our economies will require more IT providers to have hard conversations with their non-technical bosses and clients. Those conversations will need to be a genuine two-way exchange to be useful, with investment on both sides.

    So how do non-technical (or ‘accidental’) leaders figure out their preferences in IT? Right now, you have three options: do the hard translation work yourself, hire a consultant or fractional CTO to do it for you, or get a better MSP.  At Lumenas, we’re building tools to make this work easier for all IT leaders, whether technical or accidental.

    Let me know if you’ve got a story like mine or are worried you might be living one. I’d love to hear more about people’s challenges in managing IT so we can help solve them.


    This piece was originally published on Linkedin here.

  • Leading Digital – A Digital Mindset

    Leading Digital – A Digital Mindset

    A digital mindset

    Today we’re talking about mindset. You’re already across what an enormous impact the mindset of a leader has on the team – I’m sure you can think of the good, the bad and the ugly that you’ve seen in the past!

    So what kind of mindset should we bring to digital leadership? There are two qualities that are critical for success; curiosity and adaptability. Most organisations handle technology on a project basis. You scope a need, choose a tool, implement it, and move on. Others layer on system lifecycle management – tracking updates, costs, and risks.

    But if you want to get real value from technology, you need something more. You need to shift from a set-and-forget approach to asking “is it as good as it can be today?”.

    Most modern organisations rely heavily on Software as a Service (SaaS) tools. New features roll out constantly and the organisations that unlock the most value are learning, adapting, and evolving how they use those tools are used over time.

    Take Canva, for example. I use it almost every day, but if I was still using it the way I did when I first signed up, I’d be missing out on half its power. The same applies to the tools your organisation uses every day. The real value comes comes from how your people keep using and evolving with tools over time. That might look like slow shift in process over time, or complete recreation of processes as new technologies streamline them.

    The mindset shift starts with leadership. When leaders model curiosity, adaptability, and alignment between tech and business goals, teams follow. Keep reading for some quick questions you can ask to make sure you’re getting the most out of technology for your teams.

    Leaders have been asking…

    Asking great questions is a leadership skill you already have. Here’s some tech questions you can ask your team to maximise tech ROI and model curious leadership.

    When you want to encourage the team to safely share ideas: “What’s one digital tool we use that you think we could be getting more out of?”

    When you’re considering whether to upgrade to a new system: “Before we look for something new, have we gone back to first principles on mapping our business process to the features this system has?”

    When your teams need to take on a new business process: “How can we support this with our existing tech systems? Are there parts of this process we could streamline for the team?”

    Some of these questions take a little time to investigate, but it’s often a case of slowing down to speed up. Business processes change over time just as much as software features do, but we rarely go back to mapping the two out together. You might be surprised how much time you can save!

    Take action!

    This fortnight, choose one process your team does all the time, like onboarding a new client or managing approvals. Sit down with the team and ask: “Could our existing tools support this better?” Spend 30 minutes together exploring what’s possible and capture one small improvement to test this month.

    It’s a small step, but you’re signalling to the team that you care about saving them time and that it’s okay to suggest tech and process improvements.


    This piece was originally published in the Leading Digital newsletter here.